
Most enterprises handle AI governance the same way they handle data privacy compliance: assign it to legal, build a policy document, train the team, file it away. The problem is that governance for a recommendation engine is a fundamentally different problem than governance for an agent that takes actions.
When AI systems move from generating content to initiating actions, placing orders, updating records, communicating with customers, escalating tickets, modifying schedules, the financial exposure changes. You're no longer governing an output. You're governing a decision. And governing decisions is a CFO problem, not a legal problem.
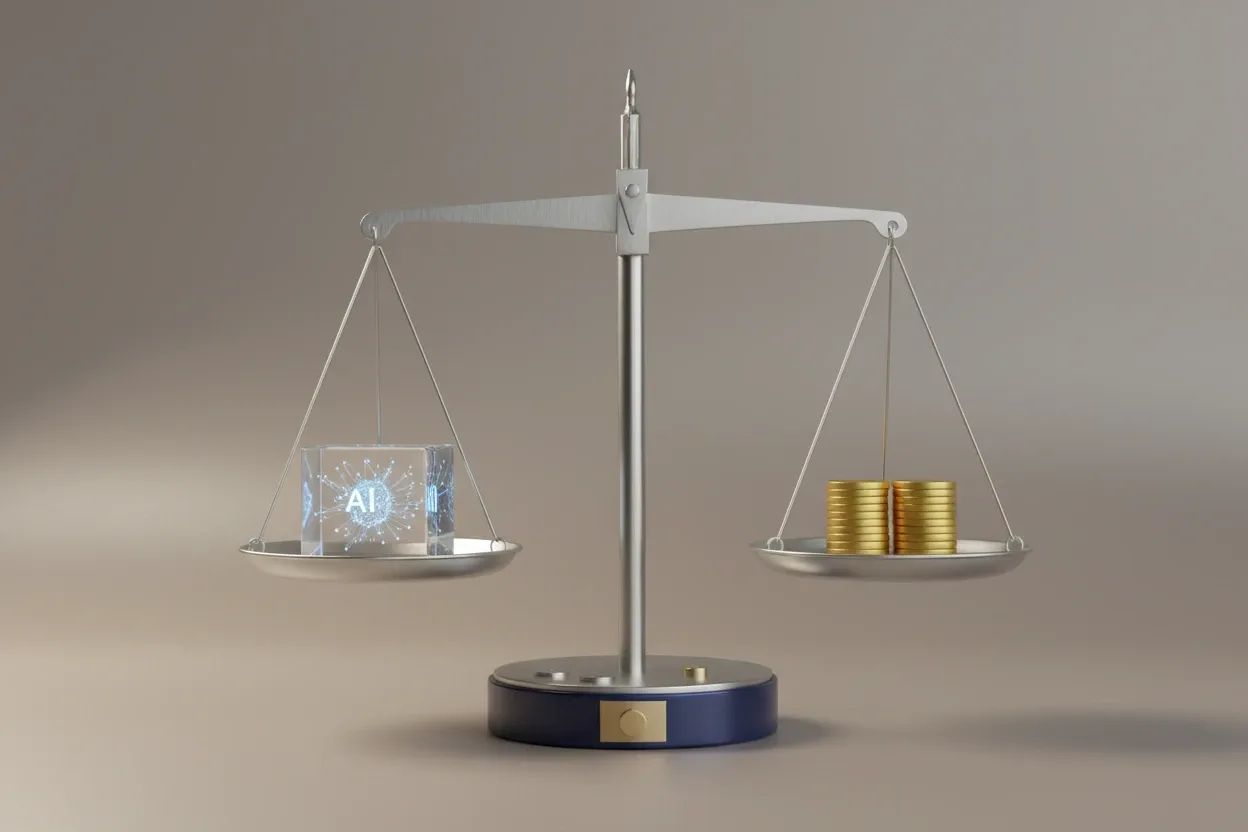
Here's the frame I use. Every autonomous AI decision carries an expected return, a control cost, and some amount of economic downside. The expected return is what the organization gains from automating that decision: speed, cost, scale, consistency. The control cost is what it takes to monitor, audit, and correct autonomous decisions. The economic downside is what happens when the decision is wrong and consequences are hard to reverse.
AI governance, in this frame, is a capital allocation question: where does the expected return justify the economic downside of autonomous action, and where should human approval remain the default?
This reframe changes what a CFO should be asking in an AI governance conversation. The relevant question isn't "does this comply with our AI policy?" It's "what is the authorized scope of autonomous action, and is that scope priced correctly relative to the risk?"
The organizing principle is consequence and reversibility. An AI system making autonomous decisions that are low-consequence and easily reversible. Routing a customer inquiry, categorizing an expense, flagging a record for review -- carries a different risk profile than one making decisions that are high-consequence or hard to undo. Approving a vendor payment. Changing a customer's contract terms. Initiating a procurement order above a certain threshold.
As consequences rise and decisions become harder to reverse, the threshold for autonomous action should rise with them. This isn't just a governance principle. It's a capital discipline. The organization is effectively accepting economic exposure every time it delegates a decision to an autonomous system. Whether that exposure is priced correctly is a financial question.
In practice, this produces three categories of AI decisions. First, decisions that can be fully autonomous -- where the consequence of error is low and the decision can be corrected quickly. Second, decisions that require human approval before execution, where consequences are meaningful enough that an accountable human should confirm before the system acts. Third, decisions that should remain human-controlled regardless of AI capability -- where the consequence of error is significant, or reversibility is limited enough, that autonomous action isn't worth the exposure.
Most organizations that have thought carefully about AI governance have something like this taxonomy. The problem is that the taxonomy gets built in legal or compliance, using risk language that doesn't connect to financial language. Nobody answers the question: what is the capital cost of getting this category wrong?
For a CFO, the governance conversation should start with the autonomy threshold, not the policy document. Which decisions is the organization prepared to let an AI system make without human approval, and what is the expected economic downside of that delegation at scale? If a system makes ten thousand autonomous decisions per day, and a small percentage carry meaningful financial exposure, the aggregate risk may be significant, even if each individual decision seems minor.
The compliance framing misses this because it evaluates decisions one at a time, against a policy, with a binary pass/fail outcome. The capital allocation framing evaluates decisions as a portfolio, against an expected value, with a continuous risk-return calculation.
Treating AI governance as a compliance problem isn't wrong. It's incomplete. An organization that has passed its AI policy audit but hasn't answered the capital allocation question, which decisions are we delegating, at what scale, with what economic exposure, has checked a box but hasn't done the governance work.